Kudankulam breach: cyber risk beyond the fence
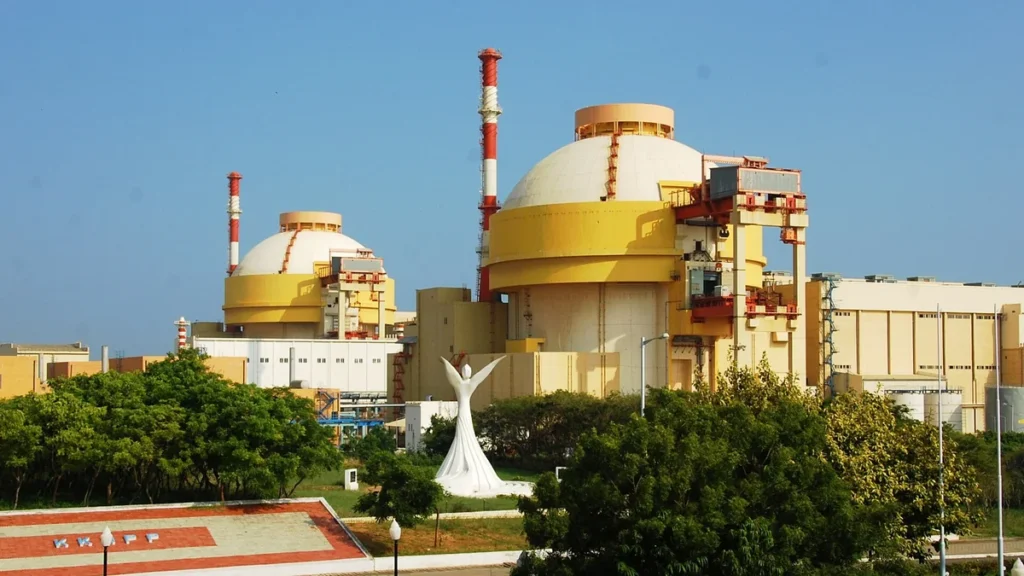
A nuclear plant can have the best fence in the country and still leak secrets from a contractor’s computer miles away. That is the lesson of the Kudankulam data breach. No reactor was hacked, but project files ended up on the dark web, the hidden part of the internet used by criminals. A researcher at MP-IDSA argues that India’s cyber rules guard the plant, not the whole chain of companies that hold its data.
- Plant
- Kudankulam, Tamil Nadu
- Leak
- About 14.3 GB, 2016–2025
- Route
- Contractor’s data centre hit by ransomware
- Reactors
- Air-gapped, no sign of access
The Kudankulam data breach: what happened?
Think of a bank that guards its vault well but lets a caterer keep a copy of the building plans. If the caterer’s office is burgled, thieves get the plans without touching the bank. Kudankulam’s story is much the same.
- A group called World Leaks posted parts of about 14.3 GB of files covering 2016–2025: drawings, supplier details, inspection records, meeting minutes and insurance papers.
- The route: Reliance Infrastructure, the contractor for Units 3 and 4, stored the data with data-centre company Yotta, which was hit by ransomware on May 29. Ransomware is malicious software that locks or steals files and demands money.
- NPCIL (Nuclear Power Corporation of India Ltd, the plant’s operator) says only non-nuclear infrastructure was affected; the control and safety systems are air-gapped, meaning not connected to the internet at all.
- This is not the first time: in 2019, Dtrack malware, linked to North Korea’s Lazarus Group, hit the plant’s administrative network.
- Kudankulam is growing to 6,000 MW, while private firms are entering defence, space and government cloud.
What is critical information infrastructure, and who protects it?
Critical information infrastructure means computer systems whose failure would badly hurt national security, the economy or public health, such as power grids, banks and nuclear plants.
Two bodies matter. NCIIPC (National Critical Information Infrastructure Protection Centre, Section 70A of the IT Act) protects such systems. CERT-In (Indian Computer Emergency Response Team, Section 70B) is the national agency that responds to cyber attacks.
The gap: duties fall on the operator of a ‘protected system’. Once data goes to a contractor, only the contract protects it. The DPDP Act covers personal data, not engineering drawings.
Who holds the data, who is responsible?
| Holder | What they had | Who regulates them |
|---|---|---|
| NPCIL (operator) | Reactors, control systems | NCIIPC duties as a protected system |
| Reliance Infrastructure (contractor) | Project drawings and records | Mostly the contract |
| Yotta (data centre) | Stored the contractor’s data | CERT-In reporting rules |
Which laws and Articles apply?
- IT Act, 2000: Section 70 (protected systems), 70A (NCIIPC), 70B (CERT-In).
- CERT-In rules: service providers, data centres and companies must report cyber incidents (UPSC 2017).
- DPDP Act, 2023: covers personal data only.
- Atomic Energy Act, 1962: nuclear power is run by the Centre through NPCIL under the Department of Atomic Energy.
Why does the Kudankulam data breach matter?
| Angle | What to note |
|---|---|
| Spy value | Drawings and supplier lists help plan a future targeted attack. |
| No owner of risk | Operator, contractor and data centre can each say ‘not my system’. |
| Outsourcing | More private vendors means more doors into sensitive data. |
| Nuclear safety | Air gaps protect reactors, but data around them still leaks. |
What are the problems with the Kudankulam data breach?
- Law protects the system, not the data that leaves it.
- Contracts rarely carry strong security duties.
- Many vendors hold more data than they need, for longer than needed.
- Repeated incidents (2019, 2026) show lessons are slow to stick.
What should be done next on the Kudankulam data breach?
- Security duties, audits and liability written into every contract: obligations must follow the data.
- Share less: each contractor gets only the data it needs, only as long as needed.
- One plan for CERT-In, NCIIPC, regulators and operators before a breach.
- Vendor red-team drills (friendly hacking tests) and zero-trust access, where no user or device is trusted by default.
What can Prelims ask on the Kudankulam data breach?
- CERT-In: Section 70B; NCIIPC: Section 70A, IT Act.
- WannaCry, Petya, EternalBlue = cyber attacks (UPSC 2018).
- Air gap: a system not connected to any outside network.
- IAEA safeguards apply to reactors using imported uranium (UPSC 2020).
How to write about the Kudankulam data breach in Mains
Practice question (15 marks, 250 words): In the digital era, critical infrastructure is not just a building behind a fence. Discuss the cyber risks from supply chains with reference to the Kudankulam data breach.
- Intro: the breach through a contractor’s data centre.
- Why it matters: reconnaissance value, accountability gap.
- Legal gaps: protected-system rules, contracts, DPDP limits.
- Way forward: obligations follow data, minimal sharing, joint framework, zero trust.
- Conclusion: secure the chain, not just the plant.
Ready lines for your answer
- “Security obligations must follow the data, not the organisation.”
- “In the digital era, critical infrastructure is not a building surrounded behind a fence; it is a layered system with many access points.”
Quotable data pointAbout 14.3 GB of Kudankulam files from 2016–2025 leaked after ransomware hit a contractor's data centre on May 29.
Exam angle
Prelims: CERT-In vs NCIIPC, ransomware, air gap, nuclear plants and States. · Mains GS-III: cyber security of critical infrastructure (Mains 2017 asked cyber threats).
Practice MCQs
Original practice questions (not PYQs).
Consider the following statements:
1. The National Critical Information Infrastructure Protection Centre (NCIIPC) functions under Section 70A of the Information Technology Act, 2000.
2. An 'air-gapped' system is physically isolated from the Internet and other unsecured networks.
3. The Digital Personal Data Protection Act, 2023 protects engineering drawings held by contractors.
How many of the above statements are correct?
Answer (b) & explanation
Statements 1 and 2 are correct. The DPDP Act covers personal data only, not engineering drawings.
The Kudankulam Nuclear Power Project is located in which State?
Answer (c) & explanation
Kudankulam is in Tirunelveli district, Tamil Nadu, built with Russian VVER reactors and run by NPCIL.
Questions students ask about this
Was the Kudankulam reactor hacked?
No. NPCIL says only non-nuclear infrastructure data leaked; the control and safety systems are air-gapped and show no sign of access.
How did the Kudankulam data leak?
Data stored by contractor Reliance Infrastructure with data-centre firm Yotta was exposed after a ransomware attack on May 29.
What is the difference between CERT-In and NCIIPC?
CERT-In (Section 70B) responds to cyber incidents nationally; NCIIPC (Section 70A) protects critical information infrastructure.
What does air-gapped mean?
A computer system kept completely separate from the internet and other outside networks.